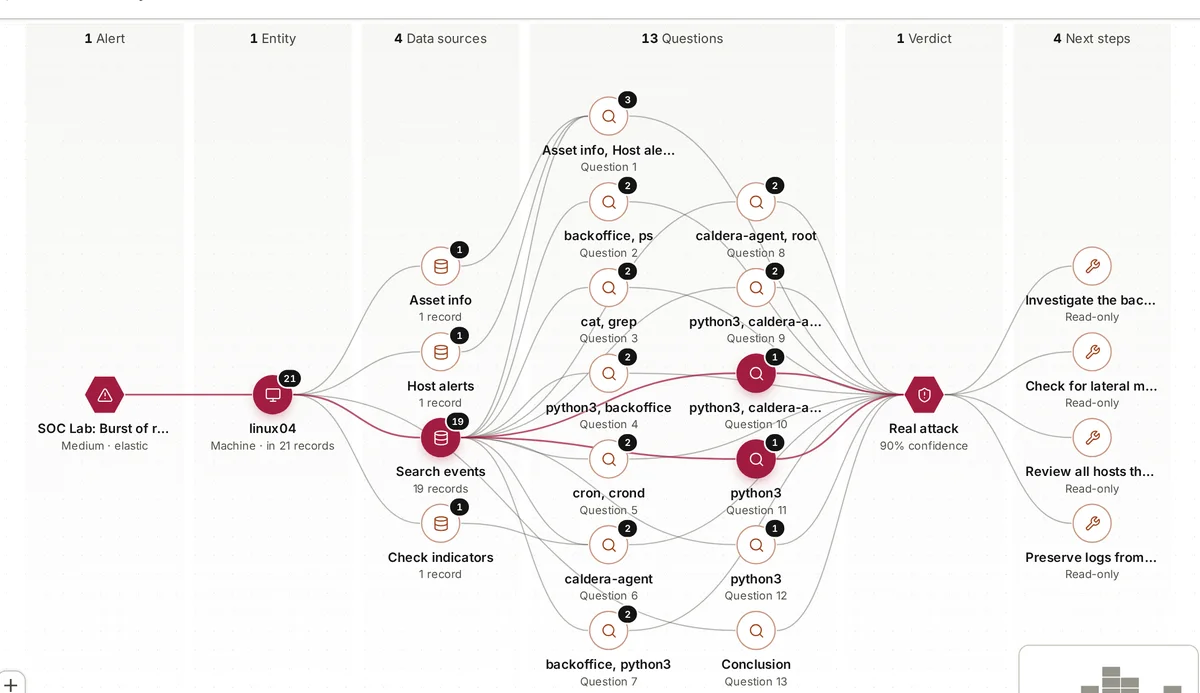
Alerts collected from Elastic Security
armor360 connects to your Elastic deployment and collects new alerts as Elastic raises them. Nothing about how Elastic detects changes: your rules keep firing as they do today. Each alert is queued, real attacks first, and given a verdict with the evidence behind it.
Elastic first, not Elastic only
Elastic Security is the first and deepest connection armor360 has. If parts of your estate report elsewhere, armor360 also collects alerts from Splunk, Microsoft Sentinel, CrowdStrike Falcon and Microsoft Defender. Alerts from every connected tool arrive in the same queue. Coverage checks and Fleet integrations are Elastic features.