Why we built it
An alert is a warning that something might be wrong. Most of the work in security operations is finding out whether it is: which machine raised it, who uses that machine, what else happened around it, and whether the places it connected to are known to be bad.
That checking is paid for in skilled staff hours, on quiet days and busy ones alike, and most of it ends with “nothing to see”. We built armor360 to take that first look, so the people who know your company spend their time on the alerts that need a decision.
What it does
armor360 collects new alerts from your Elastic security system and investigates them the way an analyst would. Each investigation ends in a plain verdict, real attack, suspicious, harmless or not sure, with how sure the agent is and the evidence behind it.
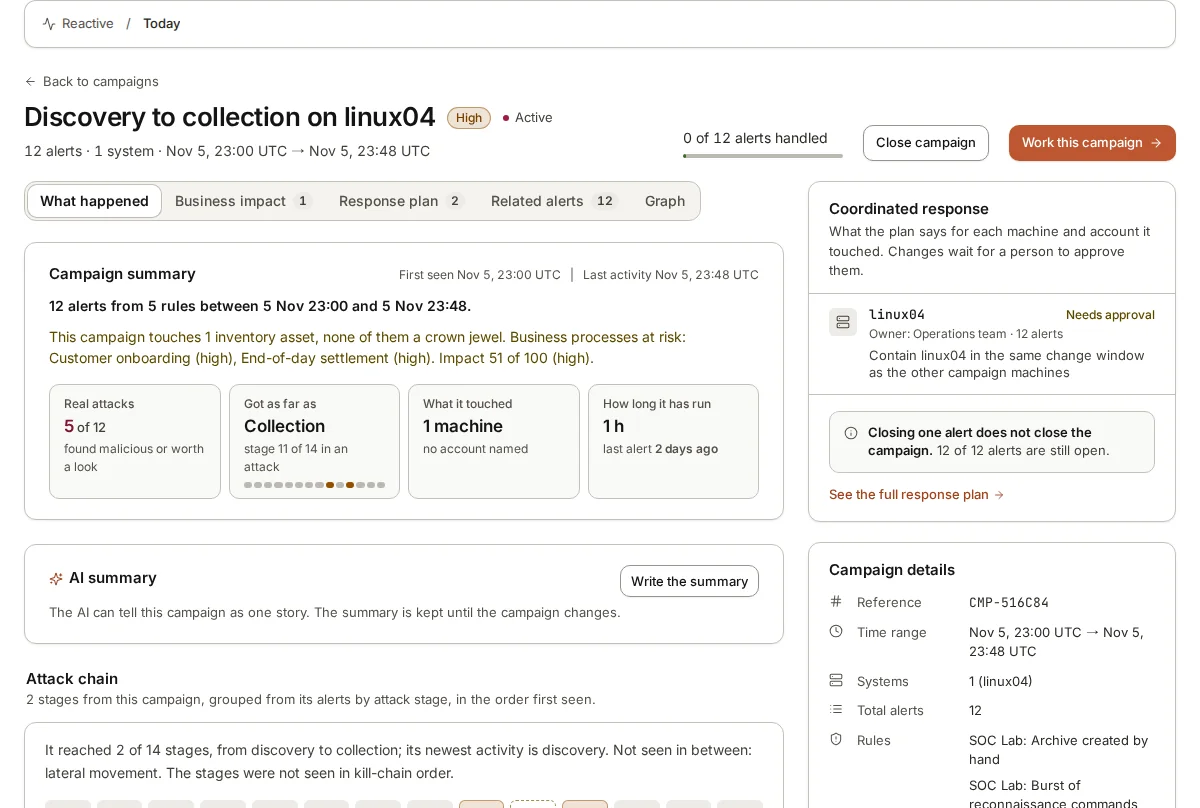
- Joins alerts that belong to the same attack into one campaign, told in order.
- Hunts your stored data for activity no rule has flagged yet.
- Shows how often a new detection rule would have fired on your past alerts before it goes live.
- Finds machines that stopped sending logs, and helps add the missing collection with Elastic Fleet.

What it leaves to people
armor360 recommends; your people decide and act. It does not isolate machines, lock accounts or block traffic. A person reads each verdict, then agrees with it or changes it, and what they say is remembered for the next investigation about your company.
Who approved what, and when, is kept in the audit trail.
Where it runs
armor360 can run inside your own environment with a language model you host, so alert data can stay within your boundaries. If you would rather not run it yourself, we can host it for you and connect it to your Elastic security system.
Get started
Pricing is by quote, sized to the machines and accounts you protect, with no charge per person. The calculator on the pricing page shows what the first look at alerts costs your team today, on numbers you can change.